VPN
Private access
Company Tools
We help companies build a secure and practical day-to-day work environment by organizing access, passwords, service requests, IT assets and team tooling in a way that supports work instead of blocking it.
Access and passwords
The first pillar is secure access to company services and resources. In practice, this usually means WireGuard or Headscale for private access, plus Bitwarden, Vaultwarden or Passbolt for password management.
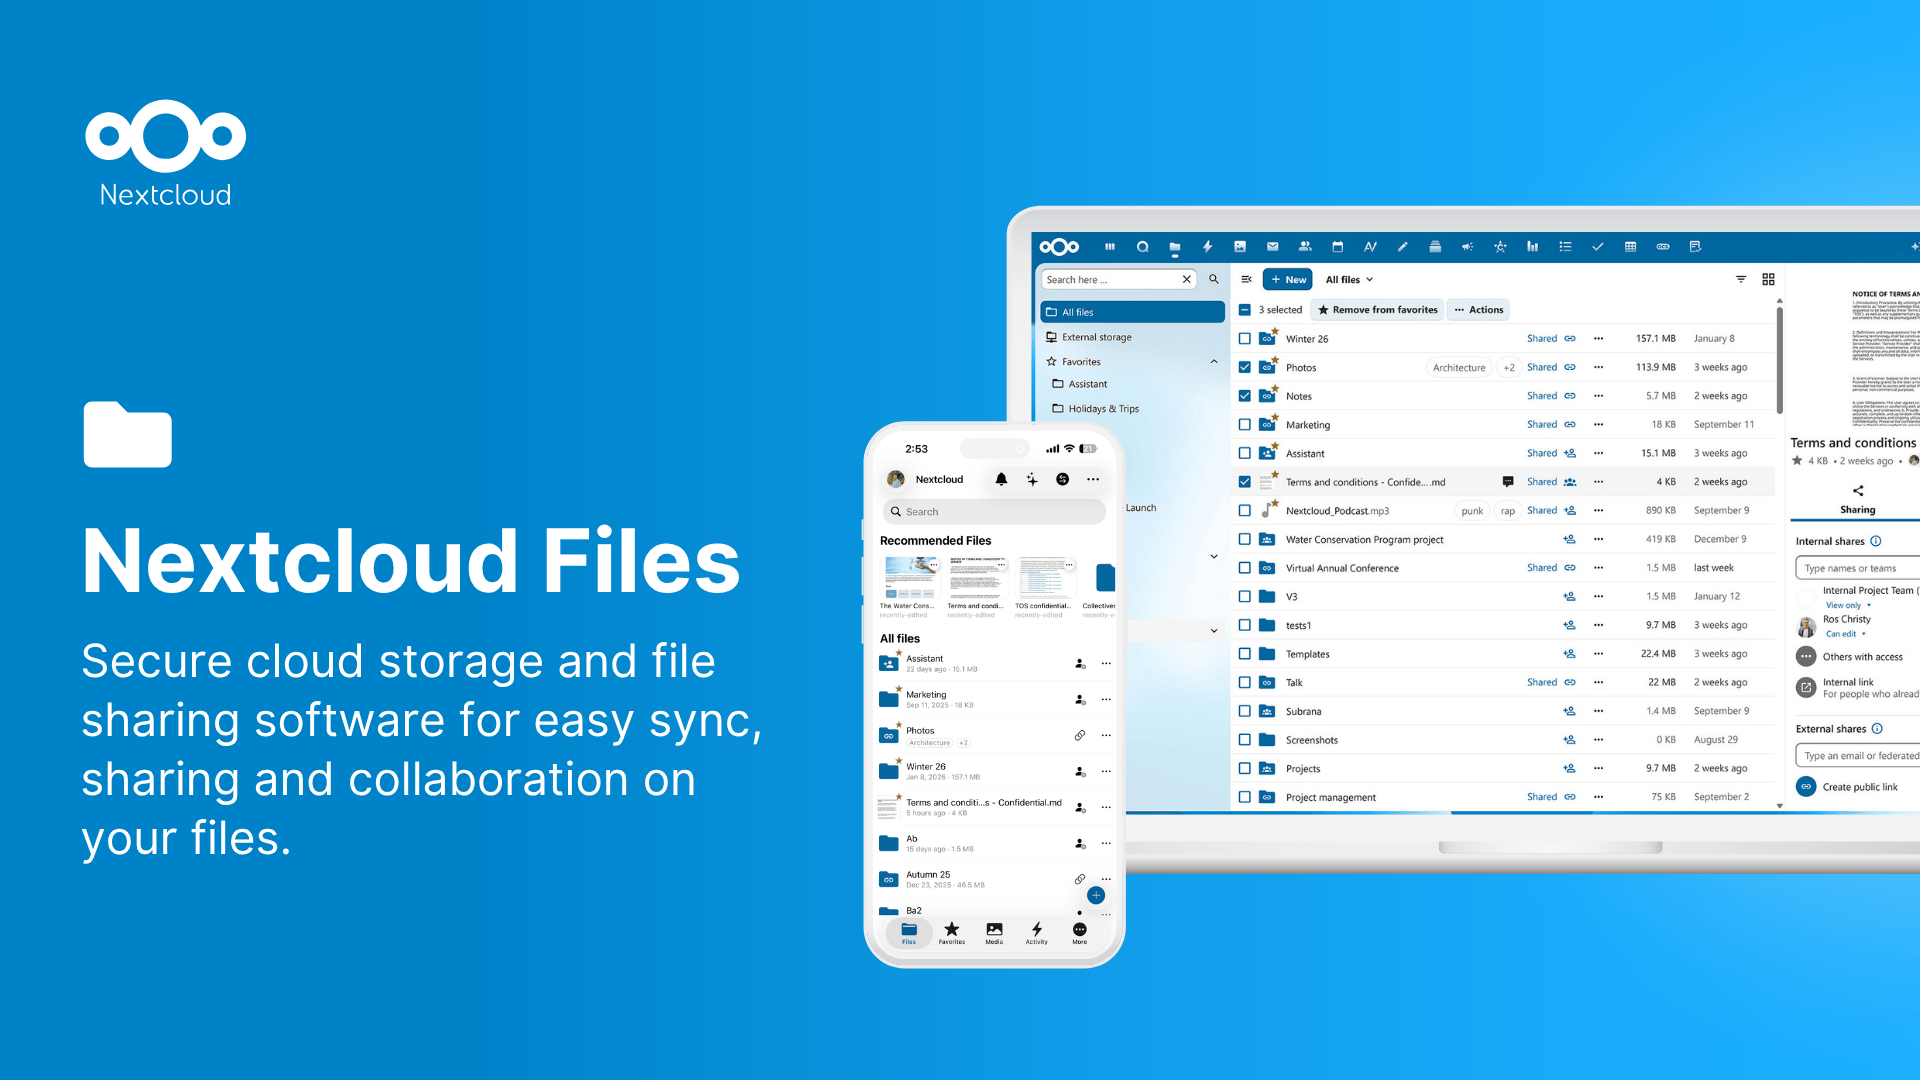
Access to admin panels, servers, NAS devices and internal services should go through a controlled private network layer, not through accidentally exposed ports.
The team needs one shared, predictable place for passwords, access and shared accounts, instead of private notes and improvised spreadsheets.
Well-chosen tooling should simplify daily work for users rather than turn security itself into a separate operational problem.
IT support and operations
The second pillar is the tooling that keeps daily operations in order: GLPI or Zammad for requests and IT support, OpenProject for projects and status tracking, Paperless-ngx for documents, and an internal knowledge base.
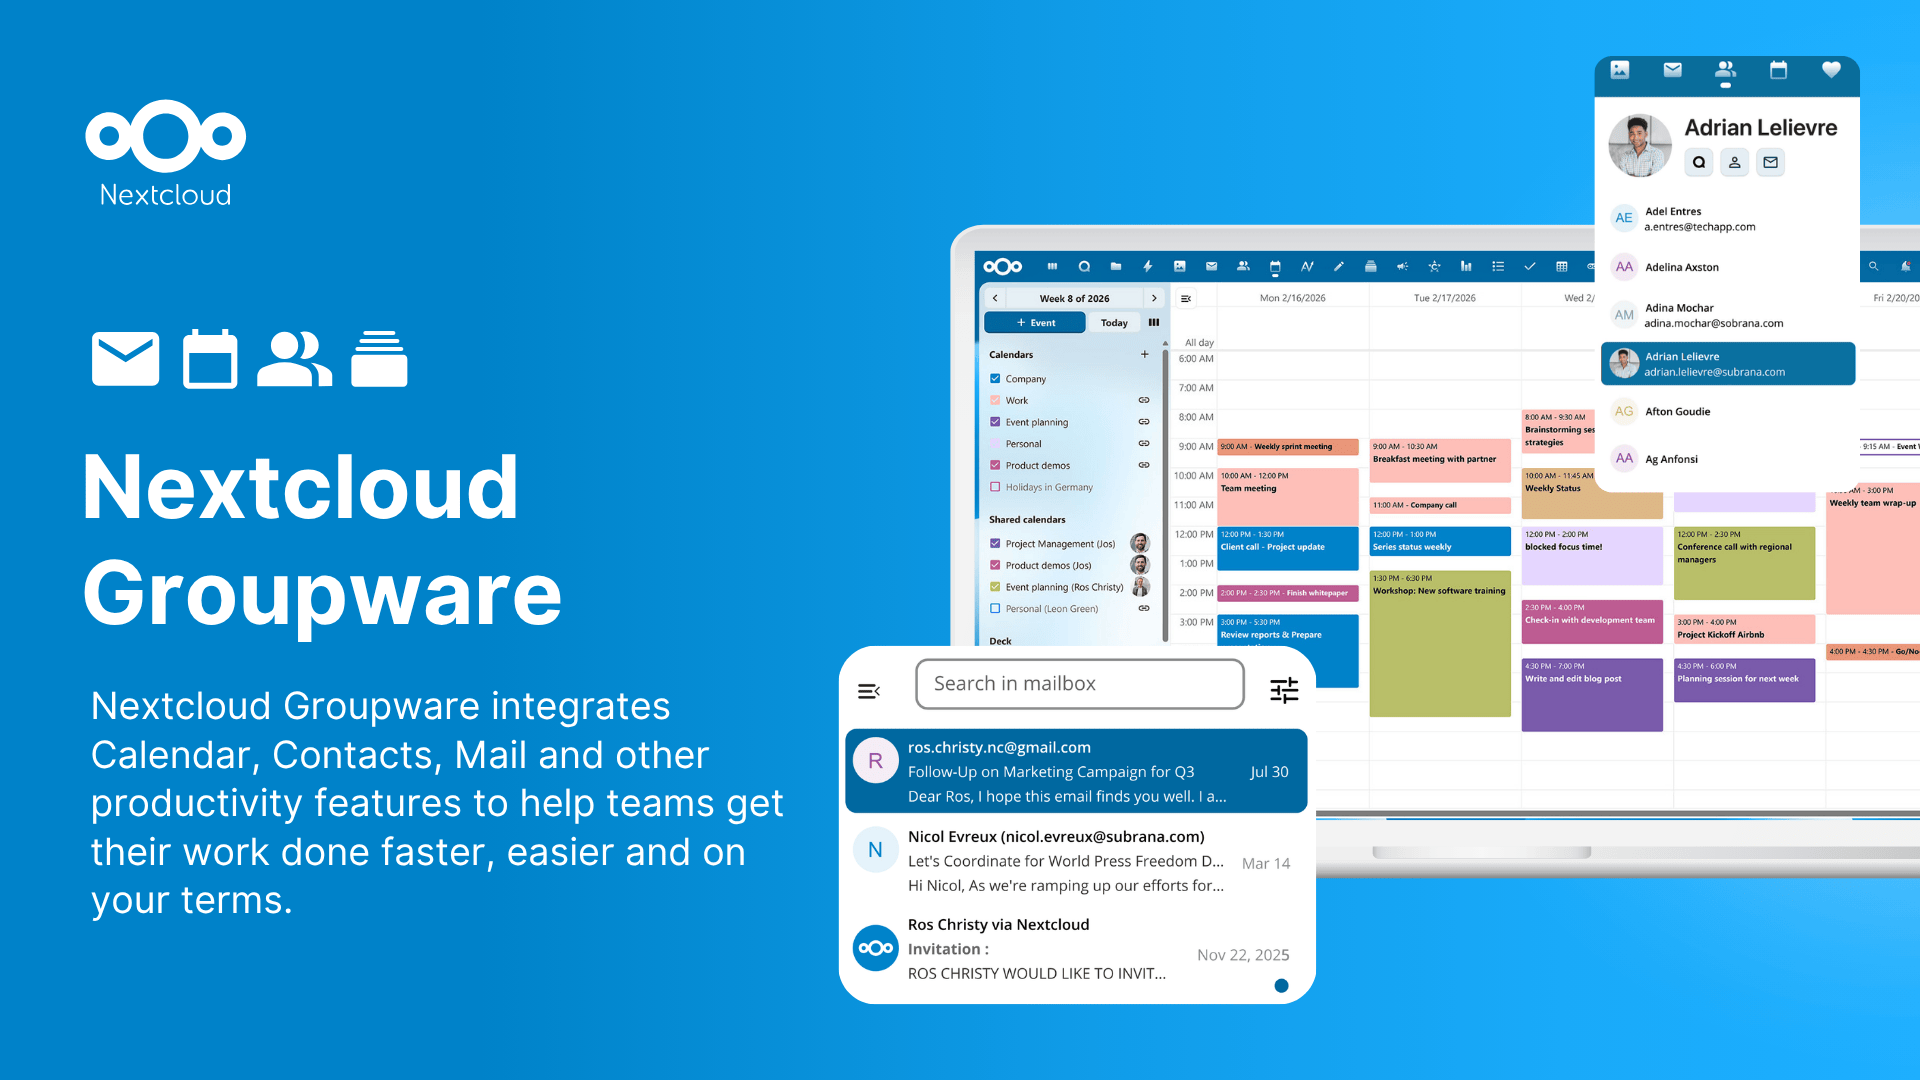
Some companies need helpdesk with asset and license inventory, while others need a simpler ticketing setup. The key is matching the tool to the way support actually works.
Projects, statuses, documents and archiving should connect with daily work, not live across separate services without a shared operating logic.
The most value appears when access, requests, knowledge, documents and collaboration operate as one organized ecosystem.
Security and daily work tools: resource access, passwords, requests, equipment and everyday team collaboration.
What connects these projects
Secure access to company resources and shared management of passwords and permissions.
Requests, IT support, equipment, licenses and ownership organized in one place; technically often through GLPI or Zammad.
Tools for daily operations, documents and procedures, such as OpenProject, Paperless-ngx and an internal knowledge base.